Underwater scene featuring a large gray cube on the seabed surrounded by colorful coral in shades of pink, orange, blue, and purple with rays of sunlight filtering down from above.A large gray cube underwater surrounded by colorful coral and sea plants in bright shades of pink, orange, blue, and purple on a sea floor with green and blue algae.

Third-Party Security For The Agentic Era

Discover who’s connected, understand what’s exposed, and take action to reduce excessive access and contain third-party threats.

The Challenge

AI Is Fundamentally Reshaping Third-Party Risk

Unprecedented Vendor Sprawl

Teams are adopting AI tools at record speeds to boost productivity, often bypassing security and risk reviews, creating a dangerous surge of Shadow AI

The Shift to Agentic Capabilities

To ensure agentic AI stays under control, organizations must continuously monitor its real-time behavior and strictly enforce risk management policies.

Deeper N-th Party Supply Chains

AI applications are built on external foundational models (like OpenAI, Google, or Anthropic), relying on external vector databases, cloud infrastructure, and third-party plugins, creating a deep web of 4th, 5th, and 6th-party dependencies.

Yesterday’s TPRM Fails in Today’s Third-Party AI Ecosystem

What Your TPRM Is Missing:

Unknown Access

What resources and data is the vendor accessing?

https://s3.amazonaws.com/webflow-prod-assets/6aac373f4b25ddfda57f90e2/6ad63efdf6eb550d350c42d5_card%201_desktop.webm
https://s3.amazonaws.com/webflow-prod-assets/6aac373f4b25ddfda57f90e2/6ad64039859385cd8554f46c_card%201_mobile.webm

AI Blindspots

What are vendor agents and LLMs doing in your environment?

https://s3.amazonaws.com/webflow-prod-assets/6aac373f4b25ddfda57f90e2/6ad63f0557dfe805ac55532b_card%202_desktop.webm
https://s3.amazonaws.com/webflow-prod-assets/6aac373f4b25ddfda57f90e2/6ad6403c4a7fd096d42738eb_card%202_mobile.webm

No Policy Enforcement

Your TPRM Policies remain on paper (not operational)
https://s3.amazonaws.com/webflow-prod-assets/6aac373f4b25ddfda57f90e2/6ad63f0c6304e502926d25f4_card%203_desktop.webm
https://s3.amazonaws.com/webflow-prod-assets/6aac373f4b25ddfda57f90e2/6ad6403f8166d81bec1d8895_card%203_mobile.webm
Underwater view from inside a dark cave opening out into deep blue water, surrounded by vibrant coral reefs in blue, pink, orange, and purple colors.Underwater cave entrance framed by colorful neon coral formations in shades of blue, orange, pink, and purple, with sandy ground leading into the dark cave interior.A black 3D object shaped like a stepped diamond floating in a colorful cave with blurred pink, blue, orange, and purple hues.Underwater cave interior with coral formations in bright pink, blue, and orange around the entrance, and water visible inside the cave.

The Great Irony

When a vendor is breached, it’s all-hands-on-deck for your security team.

They leverage every tool in the stack - except the one specifically designed for third-party risk.

Your TPRM shouldn't be sitting on the sidelines.

48%

Breaches involving a third party now account for 48% of all incidents.

$5M

The average cost of a third-party breach is about $5 million.

100%

Virtually every enterprise vendor solution now incorporates AI.

Scroll to dive

The Solution

A comprehensive platform that secures your entire vendor ecosystem, spanning direct third-parties, Nth-party dependencies, AI tools and agentic access, applying a full end-to-end risk management program:
Full Vendor Discovery Including Shadow IT and Shadow AI

Uncovers every vendor in your environment, from officially procured to unauthorized Shadow IT and hidden Shadow AI tools, to eliminate blind spots

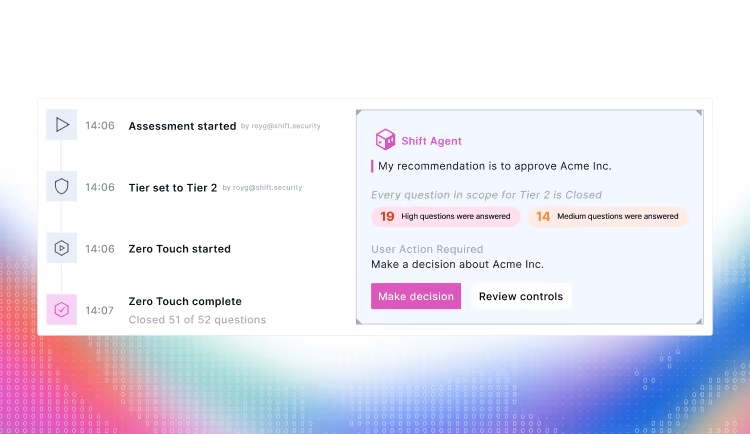
Agentic Vendor Risk Assessments  For New Vendor Onboarding

Automatic gathering of evidence-backed data, eliminating manual work and providing real-time, provable vendor risk visibility with zero friction

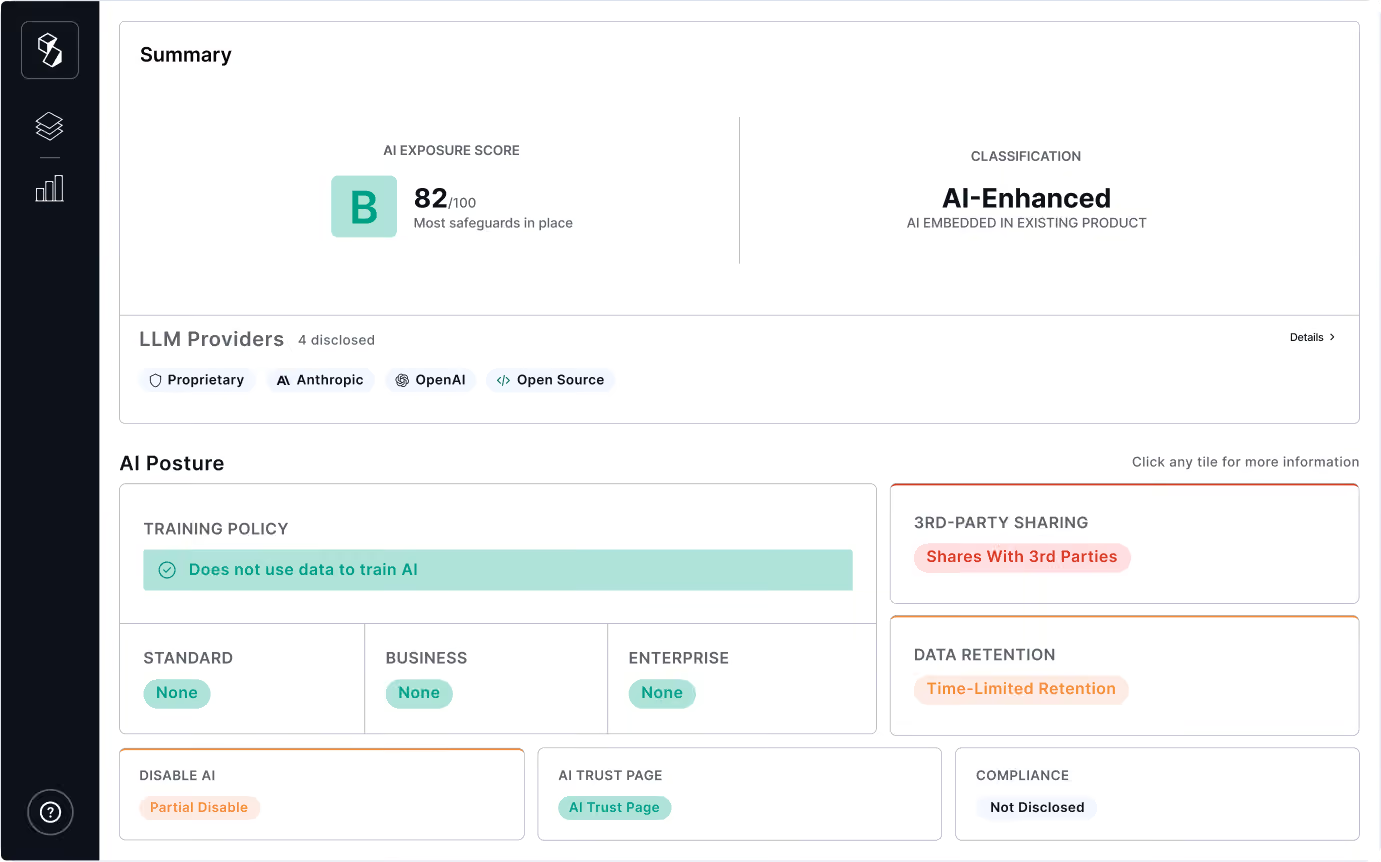
Monitor Third-Party AI Exposure and Access Drift

Uncovers hidden AI, preventing data leakage, and strictly restricting agentic access to prevent exposure of critical internal systems and data

Policy Enforcement and Attack Surface Reduction

Proactively shrink your attack surface by ensuring only authorized, secure vendors operate within your environment

Operational Third-Party Threat Detection and Response

A comprehensive platform that secures your entire vendor ecosystem, spanning direct third-parties, Nth-party dependencies, AI tools and agentic access, applying a full end-to-end risk management program:
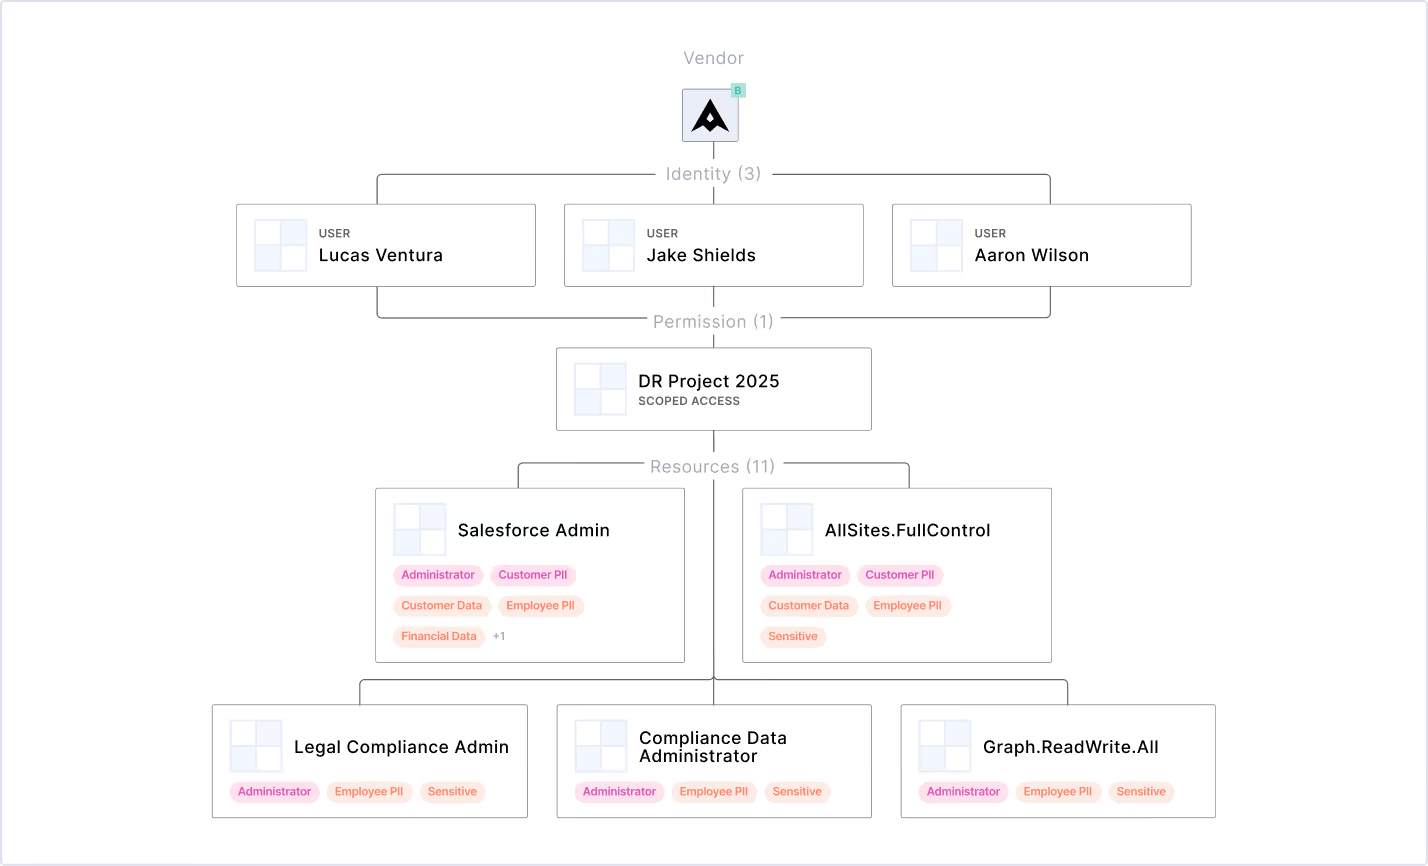
Organizational chart showing vendor 'A' with identities Lucas Ventura, Jake Shields, and Aaron Wilson under it. Below them is the permission 'DR Project 2025' with scoped access. The resources section includes Salesforce Admin and AllSites.FullControl with tags such as Administrator, Customer PII, Customer Data, Employee PII, Financial Data, and Sensitive. Under these are Legal Compliance Admin, Compliance Data Administrator, and Graph.ReadWrite.All with Administrator, Employee PII, and Sensitive tags.Diagram showing a vendor identity structure with vendor 'A' linking to users Lucas Ventura, Jake Shields, and Aaron Wilson, who have permission 'DR Project 2025' with scoped access, leading to resources including 'Salesforce Admin', 'AllSites.FullControl', 'Legal Compliance Admin', 'Compliance Data Administrator', and 'Graph.ReadWrite.All', each with associated roles and permissions blurred out.
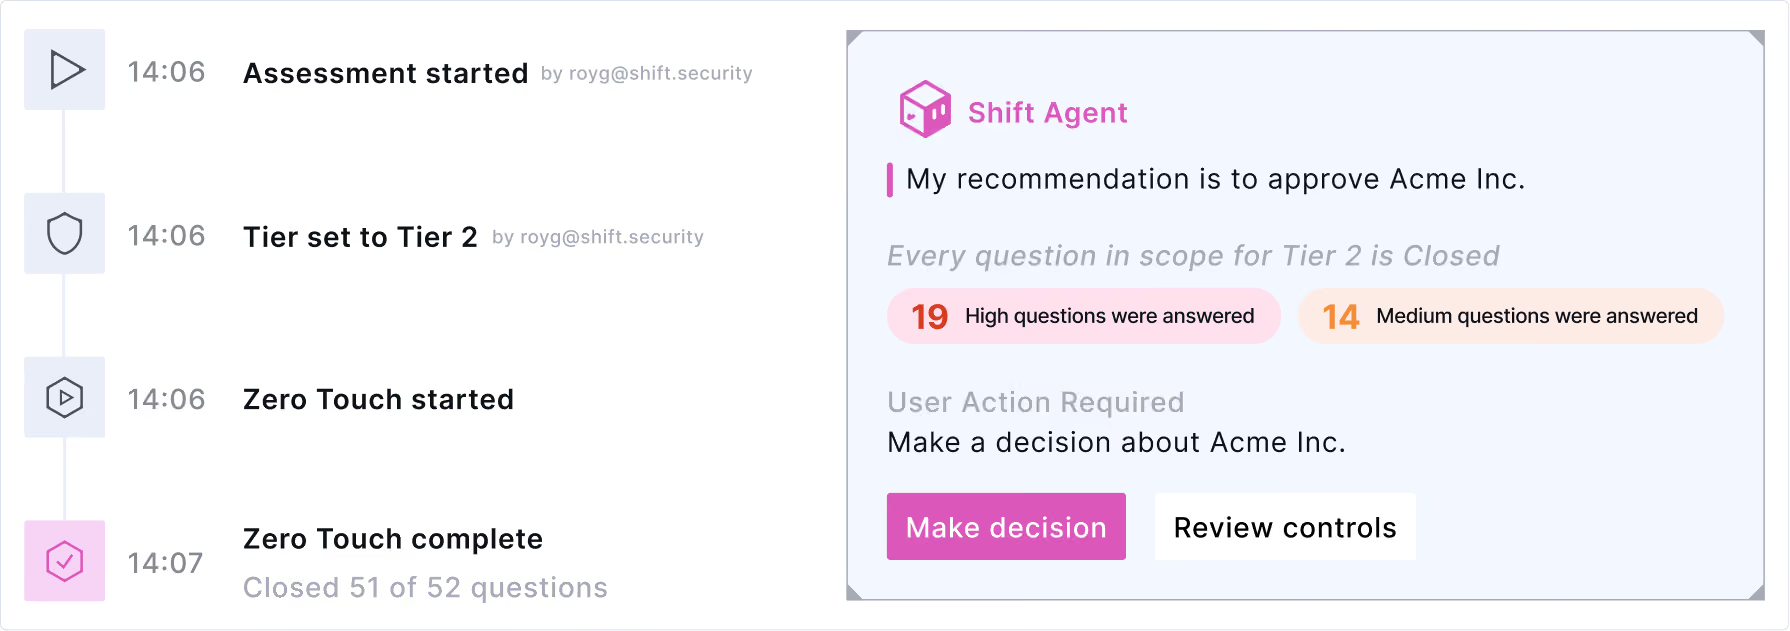
User interface showing a security assessment timeline with status updates: Assessment started, Tier set to Tier 2, Zero Touch started, and Zero Touch complete with 51 of 52 questions closed. A panel on the right from Shift Agent recommends approving Acme Inc., noting 19 high and 14 medium questions answered, and prompts the user to make a decision or review controls.Interface showing assessment progress with timestamps and status updates including 'Assessment started', 'Tier set to Tier 2', 'Zero Touch started', and 'Zero Touch complete' with 51 of 52 questions closed; recommendation panel from Shift Agent advises approving Acme Inc. with 19 high and 14 medium questions answered, and buttons to 'Make decision' or 'Review controls'.
Dashboard summary showing an AI exposure score of B (82/100) with most safeguards in place. Classification is AI-Enhanced, AI embedded in existing product. LLM providers include Proprietary, Anthropic, OpenAI, and Open Source. AI Posture section details training policy as not using data to train AI, standards as none across standard, business, and enterprise. It flags third-party sharing as sharing with 3rd parties, data retention as time-limited retention, partial disable for AI disable, AI trust page available, and compliance status not disclosed.Dashboard showing AI exposure score of 82 with grade B, classified as AI-Enhanced product, listing four disclosed LLM providers categorized by type, and AI posture details including training policy that does not use data to train AI, no standard, business, or enterprise data usage, third-party sharing noting shares with third parties, limited data retention, partial disable AI option, AI trust page, and non-disclosed compliance status.
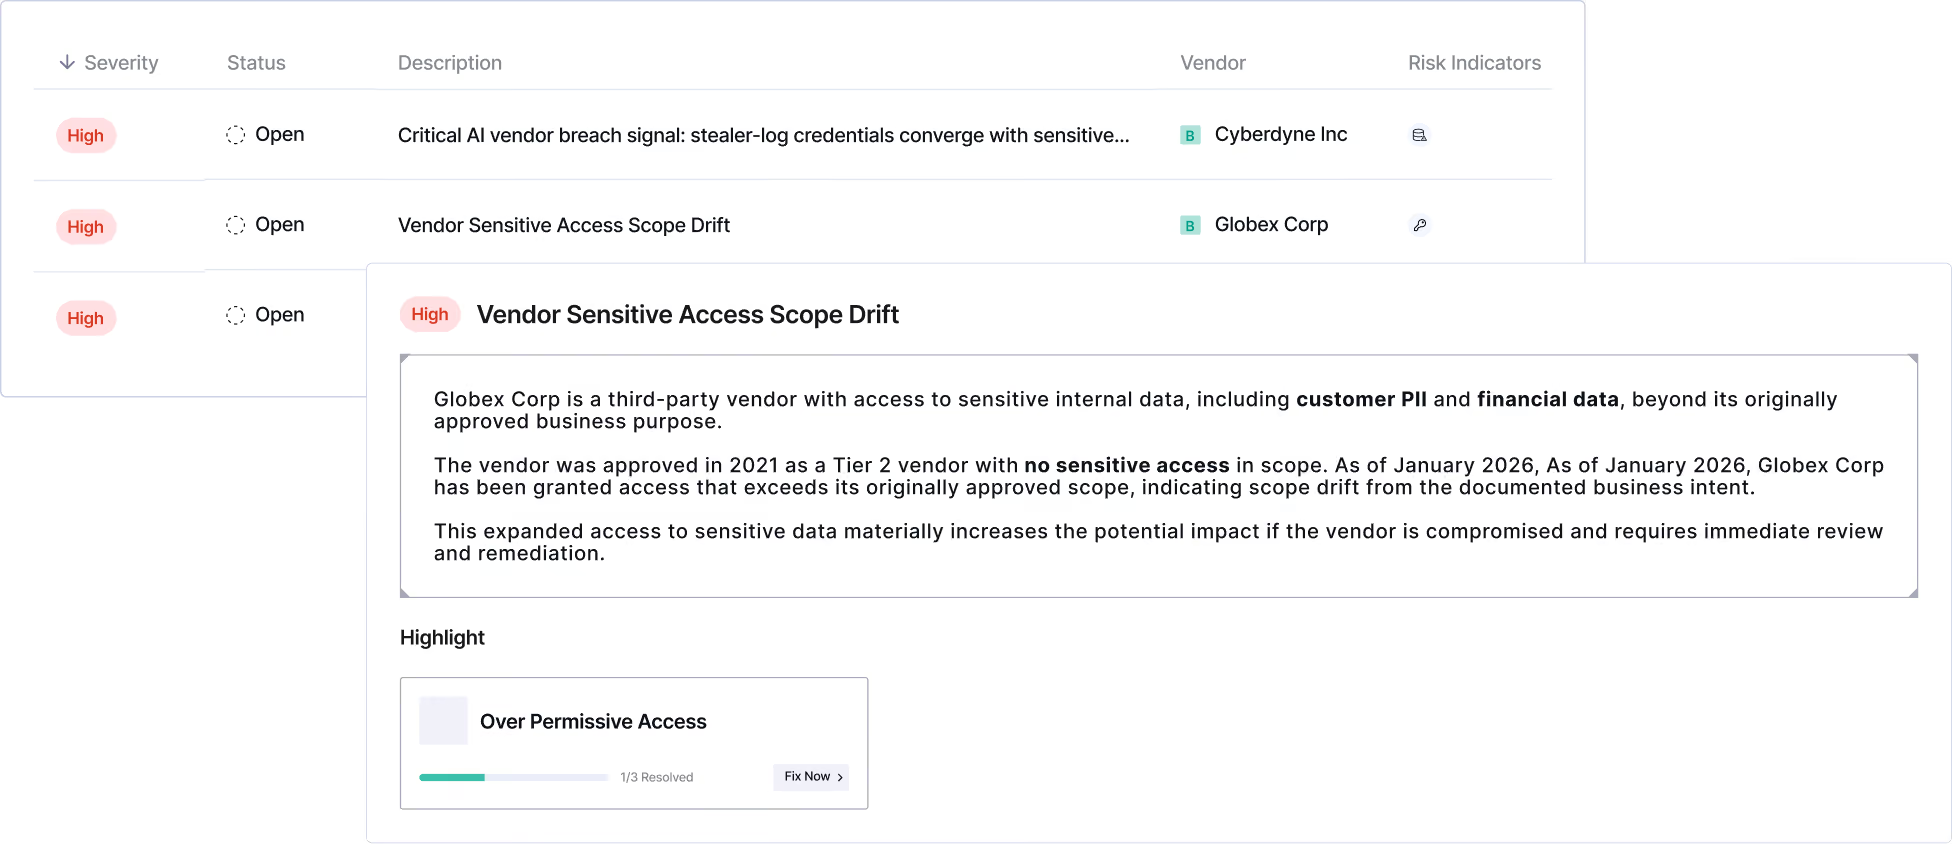
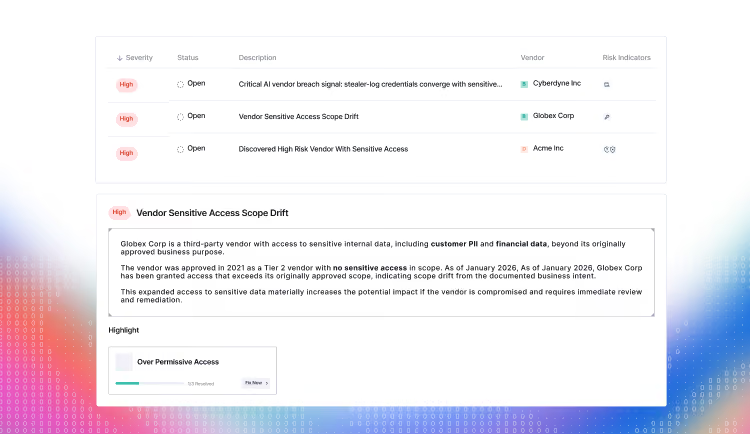
Screenshot of a vendor risk management dashboard showing three high severity open alerts for vendor sensitive access scope drift from Cyberdyne Inc and Globex Corp. Detailed view highlights Globex Corp as a third-party vendor with expanded access to sensitive internal data, including customer PII and financial data beyond approved scope, requiring immediate review and remediation. The highlight section shows a status labeled 'Over Permissive Access' with a resolution progress bar.A cybersecurity risk dashboard showing a table with three high severity open issues involving vendors Cyberdyne Inc, Globex Corp, and Acme Inc. The selected issue, 'Vendor Sensitive Access Scope Drift,' shows details about Globex Corp's expanded access to sensitive internal data like customer PII and financial data beyond originally approved scope, highlighting increased risk and need for review. A small chart labeled 'Over Permissive Access' is shown.
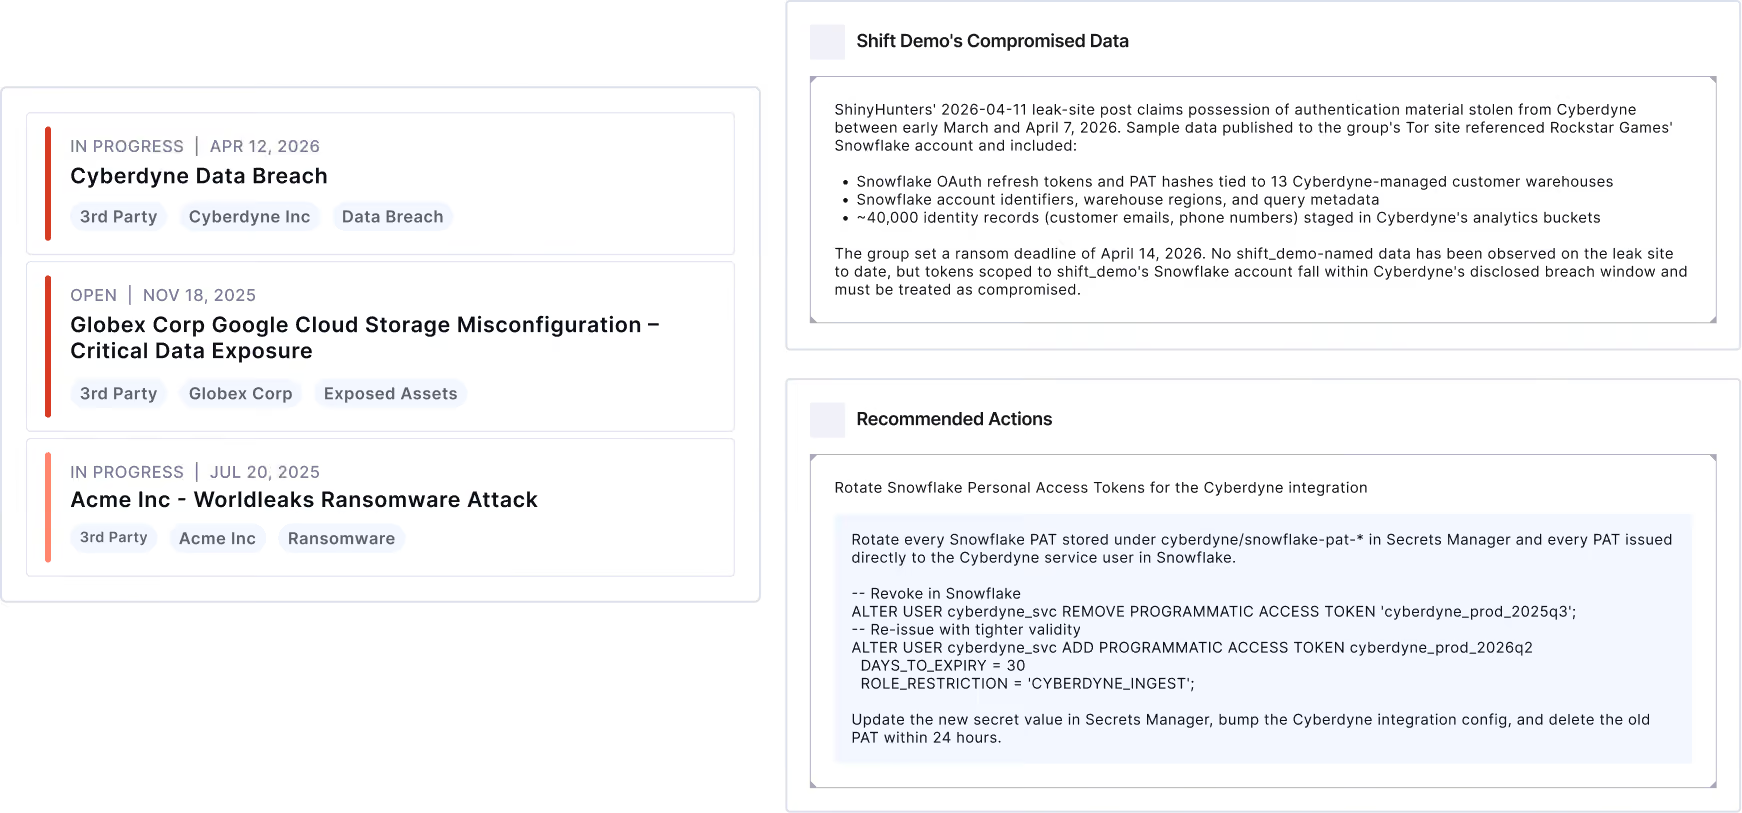
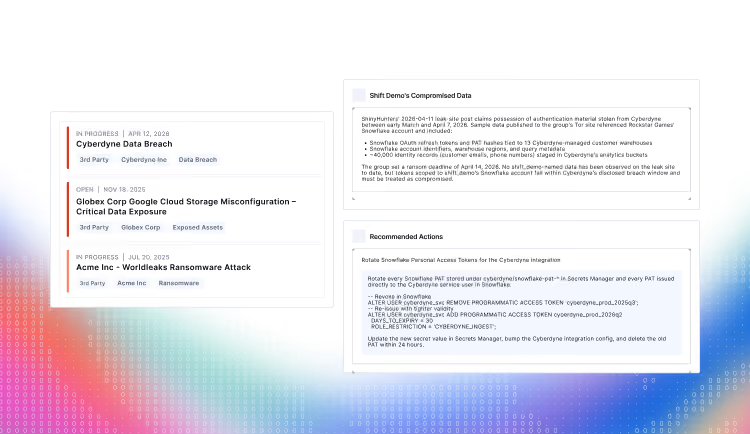
Dashboard showing three security incidents in progress: Cyberdyne Data Breach by Cyberdyne Inc on April 12, 2026; Globex Corp Google Cloud Storage Misconfiguration causing critical data exposure; and Acme Inc Worldleaks Ransomware Attack from July 20, 2025. On the right, a section titled 'Shift Demo's Compromised Data' describes a claim by ShinyHunters of stolen Snowflake tokens and data from Cyberdyne between March and April 2026. Below, recommended actions instruct rotating Snowflake personal access tokens for the Cyberdyne integration using commands to revoke, alter, and reissue tokens in Secrets Manager.Screenshot of a cybersecurity incident management interface showing three incidents: a Cyberdyne data breach in progress (April 12, 2028), a Globex Corp Google Cloud storage misconfiguration exposing data (open until Nov 18, 2025), and an Acme Inc ransomware attack in progress (July 20, 2025). The right side shows detailed text for a 'Shift Demo’s Compromised Data' involving stolen authentication data, and recommended actions for rotating Snowflake personal access tokens for Cyberdyne integration.

With Shift Security Enterprises Can Finally

Trusted By Security Leaders
Bearded man with short brown hair wearing a dark blazer and a white striped shirt, standing against a colorful digital backdrop with binary code patterns.Man with short brown hair and beard wearing a dark blazer and white shirt with thin stripes, posing against a light background with blue and pink gradient and binary code pattern.

End-to-End Risk Reduction Across the Vendor Lifecycle

“Shift brings proactive risk reduction to every phase of the third-party lifecycle, not just onboarding. It’s security-first from discovery to offboarding.”
Oliver Newbury

Former Global CISO, Barclays

Middle-aged man with short hair and a light beard wearing a grey patterned button-up shirt, smiling against a soft blue and pink gradient background with faint binary code.Smiling middle-aged man with a bald head wearing a light gray buttoned shirt with a subtle pattern, standing against a background with blue, pink, and white gradient and binary code elements.

Unprecedented Visibility into Vendor Access

“For the first time, enterprises can actually see which vendors have access to internal systems and sensitive data, monitor risky access changes in real time, and take immediate action. That’s a game-changer.”
Samir Sherif

Former CISO, F5

A Resilient Security Posture

“You can no longer secure your own perimeter and call it a day. The escalating sophistication of supply chain attacks makes Shift Security's third-party threat detection and response capabilities a critical necessity for any resilient security posture.”
Larry Slusser

Cybersecurity Executive & Strategic Advisor

Procurement never saw them. Shift did

“Reconciling Shift’s findings with our procurement systems exposed a major blind spot: 18 unprocured, high-risk vendors. We’ve since shut down eight of them, directly strengthening our compliance and security posture.”
Head of GRC, Large Investment Firm

Breach hits. Clarity follows

“Following a breach at a major service provider, Shift gave us immediate clarity. Their blast radius analysis mapped the provider’s access to our systems, enabling our incident response team to quickly assess exposure and take targeted action.”
CISO, Global Financial Services Company

Shadow AI, caught before it touches PHI

“Third-party AI exposure is a major risk to patient data. By continuously monitoring our AI footprint, Shift empowers us to stay vigilant and ensure strict adherence to HIPAA BAA requirements across our supply chain.”

Head of Third-Party Cyber Security, National Healthcare Organization